

ASUS issues WIFI Router updates to address severe vulnerabilities

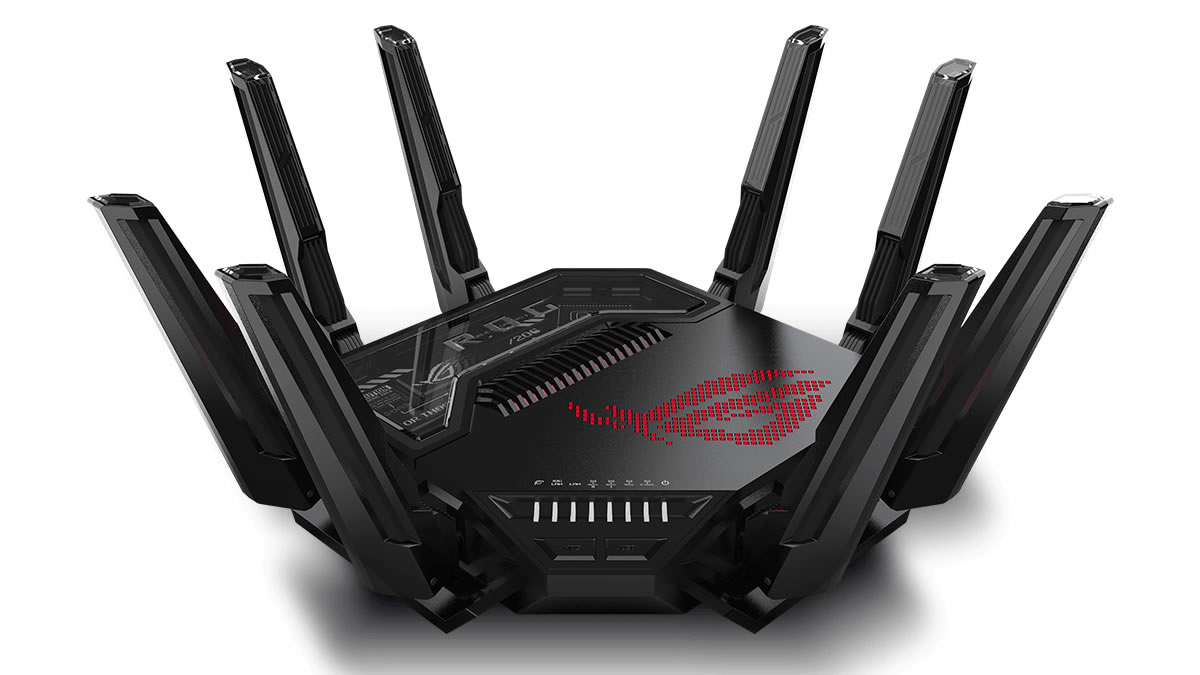
ASUS issues two sets of WIFI router fixes to address critical vulnerabilities
Over the past week, ASUS has issued two sets of WIFI router firmware updates to address two sets of vulnerabilities. The first security update was issued on October 20th for 3.0.0.4_386 series and 3.0.0.4_388 series routers, while a newer October 23rd update issued fixes for 3.0.0.6_102 series routers. Users of affected routers should update to newer firmware versions as soon as possible.
Both security reports detail different vulnerabilities for different WIFI routers. For routers with 3.0.0.6_102 series firmware, an improper authentication vulnerability exists that, under specific conditions, allows unauthenticated attackers on an adjacent network to gain administrative access to the router. For 3.0.0.4_386 series
3.0.0.4_388 series router firmwares, two security vulnerabilities are noted. If exploited, these vulnerabilities could allow an adjacent attacker to cause a denial of service on the device, obtain limited device information, or alter the device’s operating state.
Thankfully, these flaws require access to an adjacent network, which means that attackers need to be close to your router to conduct an attack. Even so, users of affected ASUS routers should update them as soon as possible.
Note that for the 3.0.0.4_386 and 3.0.0.4_388 router firmware series, ASUS has provided “EOL Guidance”. That means that these new security flaws affect some of ASUS’ unsupported router models. No updates are available for these router models, and ASUS recommends replacing them with newer models. ASUS’ Security Advisory page provides mitigation options for users who cannot update their routers.
Join the discussion on ASUS’ WIFI router security updates on the OC3D Forums.